DRIVEN BY DATA · PROTECTING WHAT MATTERS

STATISTICS. CODE. SECURITY.

Recent B.S. Statistics graduate from the University of Central Florida with a heavy CS course load and a passion for cybersecurity. Building secure, data-driven solutions on Azure and AWS — accelerated by an AI-native development workflow.

ACTIVELY SEEKING FULL-TIME CYBERSECURITY ROLES
2025 B.S. STATISTICS · UCF
4 AI CODING AGENTS DAILY
2 CLOUD PLATFORMS
10+ PROJECTS SHIPPED
∞ CURIOSITY
01

ABOUT

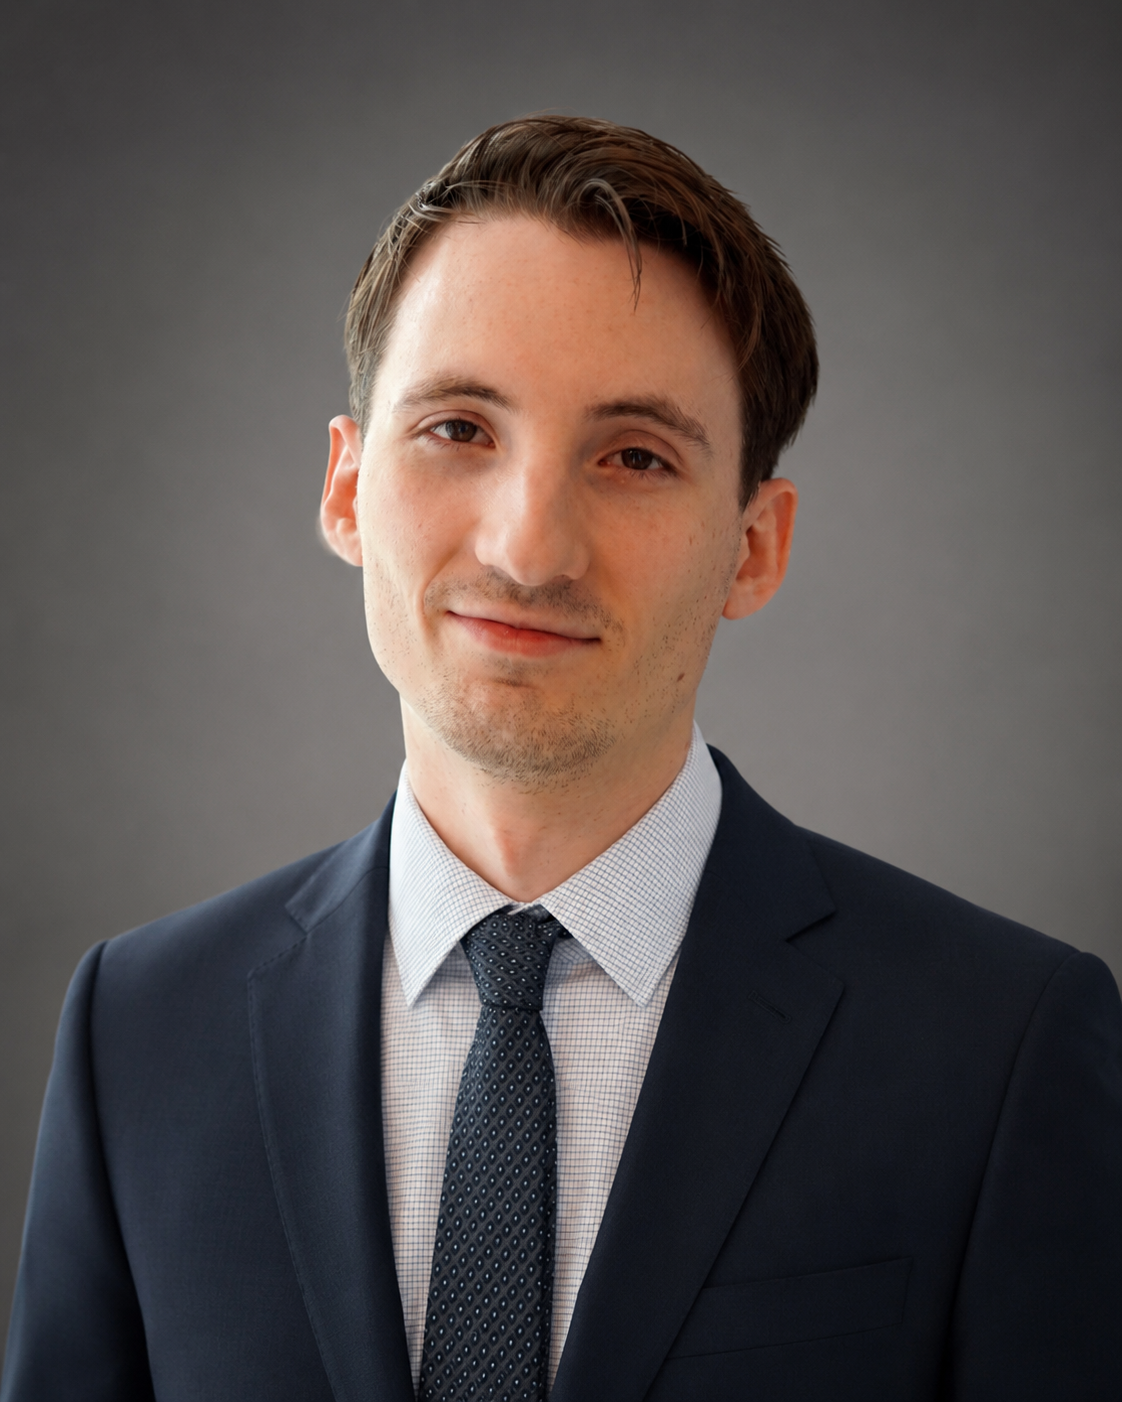
Matthew Faber
NAME Matthew Faber
BASE Riviera Beach, FL
ROLE Cybersecurity Engineer
STATUS Open to opportunities

I graduated from UCF in December 2025 with a B.S. in Statistics and a course load deep in computer science — programming in C, Java, Python, and R, statistical learning, big data analytics, and security in computing.

My focus is cybersecurity: detection engineering, threat intelligence, and the analytics that drive both. I'm building a portfolio of practical tools that solve real problems for security learners and practitioners — every project ships, gets used, and gets iterated on.

I'm AI-native. I run a daily workflow across GitHub Copilot, Claude Code, and OpenAI Codex — not as autocomplete, but as a multi-agent engineering team. It's how I ship faster than a typical new grad, with a higher standard of code review and security hygiene than I could maintain alone.

“ Statistics taught me to think in distributions. Security taught me to think in adversaries. AI taught me to think in systems. The job is to do all three. ”

02

AI-AUGMENTED ENGINEERING

I don't just use AI coding tools — I run a coordinated multi-agent workflow across four of the strongest agents and orchestration tools available, picking the right one for each phase of the build. This isn't a productivity gimmick; it's how I scale my impact as a one-person team.

AGENT 01

GitHub Copilot

In-IDE Pair Programmer
  • Inline completions across Python, TypeScript, KQL, Bicep, HTML/CSS
  • Copilot Chat for refactors, test scaffolding, and inline explanations
  • Agent mode for multi-file edits with tool calls and validation loops
  • VS Code integration with custom instructions, prompts, and skills
DAILY DRIVER VS Code
AGENT 02

Claude Code

Architect & Long-Context Reasoner
  • Whole-repo refactors and architecture reviews with long context windows
  • Spec-first development: design docs → implementation plans → code
  • Multi-step terminal tasks, build & test orchestration via CLI
  • Threat modeling and security-review passes on my own code
PLANNING CLI · Terminal
AGENT 03

OpenAI Codex

Autonomous Task Runner
  • Hand off well-scoped tasks for asynchronous, end-to-end completion
  • Cross-validation: independent implementation against Copilot output
  • Bug triage and reproduction on isolated branches before merge
  • Documentation generation and README/changelog upkeep
EXECUTION Async Agent
AGENT 04

squad

Multi-Agent Orchestrator on GHCP CLI
  • Spins up parallel GitHub Copilot CLI agents from a single terminal
  • Fan-out / fan-in workflows: same task, multiple agents, best-of diff review
  • Lets me run scoped sub-tasks in parallel without context-switching
  • Open-source tooling — great example of the GHCP CLI ecosystem maturing
ORCHESTRATION GHCP CLI OSS

MY MULTI-AGENT WORKFLOW

01
SCOPE
Claude Code drafts the design doc, threat model, and task breakdown.
→
02
BUILD
GitHub Copilot pairs with me inside VS Code for every file change.
→
03
VALIDATE
Codex re-implements critical paths independently — diffs surface bugs.
→
04
REVIEW
Claude does a final security & quality pass before I push to main.
→
05
SHIP
CI/CD to Azure Static Web Apps. Production-grade output, solo throughput.
03

SKILLS

[ LANGUAGES ]

  • Python
    Primary language — statistical computing, automation, API integrations, Azure Functions, project scripting.
  • SQL
    Coursework + project data layers. Joins, aggregations, window functions, schema design.
  • R
    Statistics coursework throughout the degree — regression, statistical learning, biostatistics, statistical theory.
  • Java
    UCF Object-Oriented Programming (COP 3330). Classes, inheritance, polymorphism, common design patterns.
  • C
    UCF Intro to Programming with C (COP 3223C). Pointers, memory management, low-level systems thinking.
  • KQL
    Microsoft Sentinel detection writing. The query language behind the MITRE → Sentinel Detection Mapper project.
  • HTML · CSS · JS
    Personal portfolio, project frontends, D3.js visualizations. This site is hand-rolled.

[ CLOUD & SECURITY ]

Microsoft Azure Microsoft Sentinel Microsoft Defender Entra ID Microsoft Purview Azure Static Web Apps Azure Functions Azure Storage Azure Monitor AWS Route 53 AWS IAM MITRE ATT&CK NIST CSF CVE / NVD Threat Intelligence Detection Engineering

[ DATA & ML ]

Statistical Learning Statistical Theory Big Data Analytics Biostatistics Numerical Methods Linear Algebra Data Visualization Power BI pandas · NumPy scikit-learn

[ ENGINEERING & AI ]

GitHub Copilot Claude Code OpenAI Codex squad (GHCP CLI) Git · GitHub VS Code REST APIs JSON · STIX CI/CD Bicep · IaC Markdown
04

PROJECTS · TRACK RECORD

A portfolio of working tools at the intersection of cybersecurity, data, and cloud. Every featured project is shipped to a live GitHub Pages URL, open-sourced on GitHub, and built with the AI workflow above.

P-01
FLAGSHIP

MITRE → Sentinel Detection Mapper

Maps MITRE ATT&CK techniques to Sentinel-friendly detection ideas and starter KQL. Genuinely useful to working SOC teams — not just a study aid.

Sentinel KQL MITRE ATT&CK GitHub Pages
P-02
FEATURED

SC-900 Concept Map Explorer

Interactive D3.js graph connecting Microsoft security, identity, and compliance concepts. Clickable nodes expand into definitions and links to official documentation.

D3.js SC-900 GitHub Pages
P-03
FEATURED

Threat Actor Cards

Trading-card-style profiles of major threat actors — nation-state origin, target sectors, common TTPs, and linked MITRE techniques. The F1-card aesthetic translates perfectly here.

Threat Intel MITRE GitHub Pages
P-04
FEATURED

MITRE Technique Explorer

Searchable, filterable browser of MITRE ATT&CK techniques. Filter by tactic, platform (Windows · Linux · Cloud), and detection difficulty — the kind of utility blue teamers reach for daily.

MITRE JavaScript GitHub Pages
P-05
FEATURED

Compliance Framework Compare

Side-by-side reference for NIST CSF, ISO 27001, SOC 2, and CIS Controls. Filter by control category and see how the frameworks map to each other — a strong GRC signal.

GRC NIST · ISO · SOC 2 · CIS GitHub Pages
P-06
FEATURED

IR Playbook Trainer

Branching incident-response tabletop with consequence-driven paths and replayable scenarios. Pure JS state machine — no backend — teaching real IR sequencing and trade-offs.

Incident Response JavaScript GitHub Pages

ALSO IN THE GARAGE — ALL LIVE ON GITHUB PAGES

05

EDUCATION & CREDENTIALS

DEGREE

Bachelor of Science · Statistics

University of Central Florida
Graduated December 2025 · Orlando, FL

Statistics major with a substantial computer-science course load — programming in C, Java, Python, and R, plus statistical learning, big data analytics, and security in computing.

CERTIFICATIONS

Certification Progress

  • AZ-900 · Microsoft Azure Fundamentals
    COMPLETED
  • SC-900 · Microsoft Security, Compliance & Identity Fundamentals
    COMPLETED
  • SC-200 · Microsoft Security Operations Analyst
    IN PROGRESS
  • CompTIA Security+
    IN PROGRESS

APPLIED COURSEWORK · UNDERGRADUATE RESEARCH & INDEPENDENT STUDY

Selected UCF coursework, framed around the applied problem each course let me dig into. Each is grounded in real assignments, projects, and self-directed extensions.

Security in Computing CIS 3360

Studied attack surfaces, cryptography, authentication, and defense-in-depth — the foundation for my detection-engineering portfolio.

Statistics Data Science / AI I STA 4364

Hands-on with ML pipelines, evaluation, and reproducible analysis — the techniques I'm now applying to anomaly detection.

Statistical Learning STA 4241

Regression, classification, regularization, and model selection — directly applicable to detection model tuning and false-positive reduction.

Big Data Analytics Methods STA 4724

Large-scale data processing and analytical workflows — the toolkit for working with security telemetry at scale.

Biostatistical Methods STA 4173

Earned an A applying hypothesis testing and modeling to real datasets — translates cleanly to security baseline-vs-anomaly analysis.

Statistical Theory I & II STA 4321 / 4322

Probability, distributions, estimation, and inference — the mathematical backbone for anything from detection scoring to risk modeling.

Computer Science I COP 3502C

Data structures, algorithms, and complexity analysis — the foundation for everything I build today.

Object-Oriented Programming COP 3330

Java OOP design — classes, inheritance, polymorphism, and the patterns that show up across modern enterprise security tooling.

Computer Logic & Organization CDA 3103C

Low-level systems thinking: how CPUs, memory, and instruction sets actually behave — useful context for reverse engineering and exploit basics.

Discrete Structures COT 3100C

Earned an A in the math behind cryptography, automata, and graph algorithms — the formal underpinning of computer security.

Numerical Calculus COT 4500

Numerical methods, error analysis, and computational techniques — the practical bridge between math theory and working code.

Matrix & Linear Algebra MAS 3105

Linear systems, eigenvalues, and matrix decomposition — the math behind ML, dimensionality reduction, and modern detection algorithms.

Writing for the Technical Professions ENC 3241

Technical writing fundamentals — documenting decisions clearly, which is half the job in any security team.

Computer Processing of Statistical Data STA 4102

Reproducible statistical computing — the discipline that translates directly to scripting security telemetry workflows.
06

CURRENT LAP · CAREER JOURNEY

GRID
Curiosity sparked interest in data & technology
PIT STOP 1
Learned statistics, programming fundamentals at UCF
PIT STOP 2
Built projects, solved real-world problems
CURRENT LAP
Cybersecurity & cloud — detection, protection, AI-augmented engineering
NEXT LAP
Contribute to a dynamic security team and make an impact
FINISH LINE
Build, secure, and lead meaningful solutions
07

LET'S CONNECT

Looking to bring statistical rigor, security thinking, and an AI-native build process to a team that ships. If that's you, here's how to reach me.

EMAIL
matthew.t.faber@gmail.com
→
LINKEDIN
/in/fabermatthew
→
GITHUB
MTFUCF
→
PHONE
(407) 961-3073
→
BASE
Riviera Beach, FL
◆
STATUS
Available immediately
◆